Token Endpoint#
Token endpoint is an OAuth2 protected endpoint that is used to grant tokens to client in response to valid request. Token endpoint is defined in the OAuth 2.0 framework, OpenID Connect specification and other specifications relevant to them.
Tokens issued by this endpoint depend on the grant type, requested scopes, and applicable client and server configuration. The endpoint processes grant types supported and enabled by the running server.
The Implicit Grant is a legacy flow in which access tokens are issued directly from the authorization endpoint rather than the token endpoint. It is not recommended for new integrations and is not included in the default supported grant types.
Based on request, this endpoint can grant following types of tokens:
URL to access token endpoint on Janssen Server is listed in the response of Janssen Server's well-known configuration endpoint given below.
https://janssen.server.host/jans-auth/.well-known/openid-configuration
token_endpoint claim in the response specifies the URL for userinfo endpoint. By default, userinfo endpoint looks
like below:
https://janssen.server.host/jans-auth/restv1/token
In response to a valid request, the token endpoint returns token/s in JSON format similar to below. This is just a sample response. Actual response can greatly vary in its contents based on request:
  HTTP/1.1 200 OK
  Content-Type: application/json
  Cache-Control: no-store
  Pragma: no-cache

  {
   "access_token": "SlAV32hkKG",
   "token_type": "Bearer",
   "refresh_token": "8xLOxBtZp8",
   "expires_in": 3600,
   "id_token": "eyJhbGciOiJSUzI1NiIsImtpZCI6IjFlOWdkazcifQ.ewogImlzc
     yI6ICJodHRwOi8vc2VydmVyLmV4YW1wbGUuY29tIiwKICJzdWIiOiAiMjQ4Mjg5
     NzYxMDAxIiwKICJhdWQiOiAiczZCaGRSa3F0MyIsCiAibm9uY2UiOiAibi0wUzZ
     fV3pBMk1qIiwKICJleHAiOiAxMzExMjgxOTcwLAogImlhdCI6IDEzMTEyODA5Nz
     AKfQ.ggW8hZ1EuVLuxNuuIJKX_V8a_OMXzR0EHR9R6jgdqrOOF4daGU96Sr_P6q
     Jp6IcmD3HP99Obi1PRs-cwh3LO-p146waJ8IhehcwL7F09JdijmBqkvPeB2T9CJ
     NqeGpe-gccMg4vfKjkM8FcGvnzZUN4_KSP0aAp1tOJ1zZwgjxqGByKHiOtX7Tpd
     QyHE5lcMiKPXfEIQILVq0pc_E2DzL7emopWoaoZTF_m0_N0YzFC6g6EJbOEoRoS
     K5hoDalrcvRYLSrQAZZKflyuVCyixEoV9GfNQC3_osjzw2PAithfubEEBLuVVk4
     XUVrWOLrLl0nx7RkKU8NXNHq-rvKMzqg"
  }
More information about request and response of the token endpoint can be found in the OpenAPI specification of jans-auth-server module.
Configuration Properties#
Token endpoint and tokens issued by token endpoint can be further configured using Janssen Server configuration properties listed below. When using
Janssen Text-based UI(TUI) to configure the properties,
navigate via Auth Server->Properties.
- tokenEndpoint
- tokenEndpointAuthMethodsSupported
- tokenEndpointAuthSigningAlgValuesSupported
- accessTokenLifetime
- checkUserPresenceOnRefreshToken
- defaultSignatureAlgorithm
- forceOfflineAccessScopeToEnableRefreshToken
- grantTypesSupported
- accessTokenSigningAlgValuesSupported
- idTokenEncryptionAlgValuesSupported
- idTokenEncryptionEncValuesSupported
- idTokenFilterClaimsBasedOnAccessToken
- idTokenLifetime
- idTokenSigningAlgValuesSupported
- accessTokenSigningAlgValuesSupported
- legacyIdTokenClaims
- strictTokenRedirectUriValidation
- mtlsTokenEndpoint
- openidScopeBackwardCompatibility
- persistIdToken
- persistRefreshToken
- refreshTokenExtendLifetimeOnRotation
- refreshTokenLifetime
- responseTypesSupported
- skipRefreshTokenDuringRefreshing
- refreshTokenLifetime
Client Authentication#
Janssen Server Token Endpoint requires confidential clients to authenticate using one of the supported client authentication method listed below:
- client_secret_basic
- client_secret_post
- client_secret_jwt
- private_key_jwt
Refer to Client Authentication section of OpenID Connect core specification for more details on these authentication methods.
AS provides ability to customize Client Authentication behavior via Client Authentication custom script
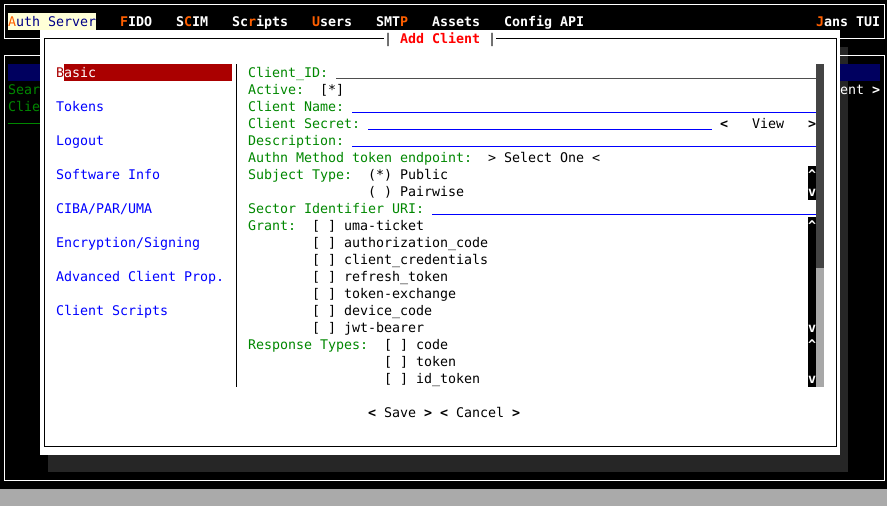
Client can specify the default authentication method. To set default authentication method using
Janssen Text-based UI(TUI),
navigate via Auth Server->Clients->Add Client->Basic-> Authn Method Token Endpoint.
Supported Grant Types#
Token endpoint supports below mentioned grant types.
- Authorization Code
- Refresh Token
- Client Credentials
- Token Exchange
- Transaction Tokens
- Device Grant
- JWT Grant
- UMA
- CIBA
- Password (legacy; not recommended).
Not in the default
grantTypesSupported. AddpasswordtograntTypesSupportedand to the client's grant types to use it.
The Implicit grant (legacy) does not use the token endpoint. Its tokens come from the authorization endpoint.
Client can configure all the possible grant types it can request from token endpoint during client configuration.
To select the available grant types using
Janssen Text-based UI(TUI),
navigate via Auth Server->Clients->Add Client/search client->Basic-> Grant.
Interception Scripts#
Token endpoint response can be further customized using interception scripts. Following interception scripts are relevant to token endpoint:
Client can configure a particular script to be executed using client configuration. To update configuration using
Janssen Text-based UI(TUI) navigate via Auth Server->Clients->Add Client/search->
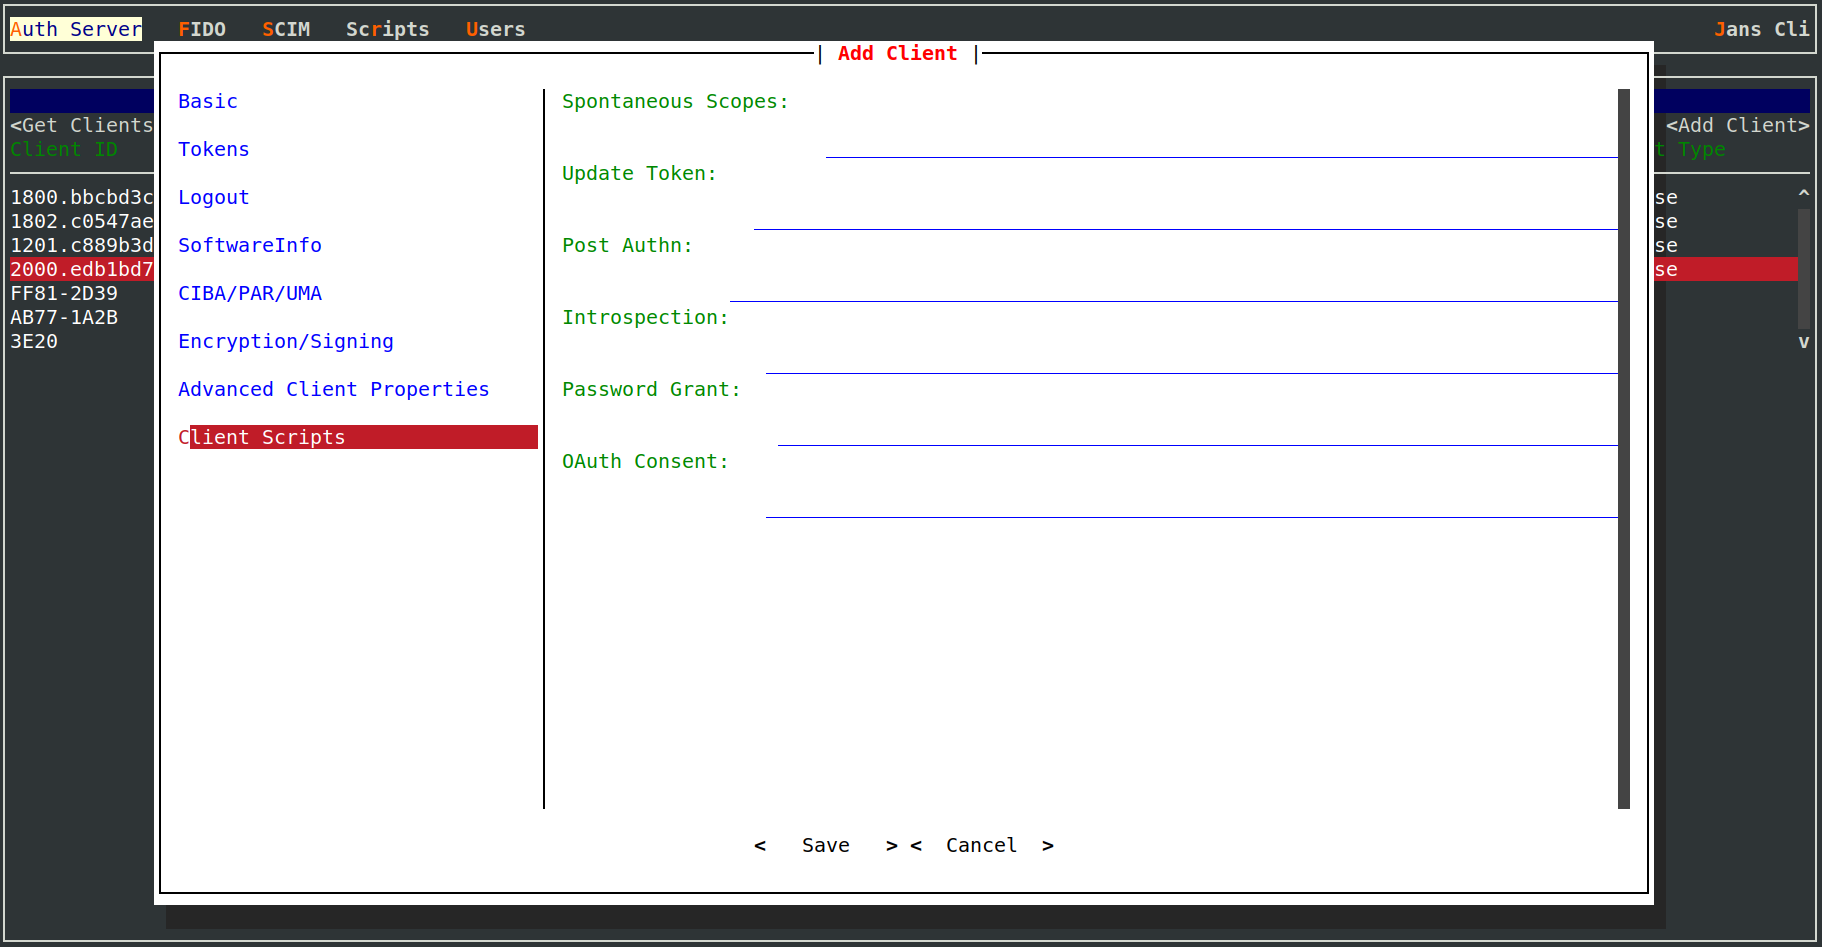
Client Scripts